October hands HR and IT leaders the same problem every year. Mandatory security training lands in the inbox, and a busy workforce tunes it out. Verizon’s 2026 Data Breach Investigations Report found a human element in 62 percent of breaches, up from 60 percent the year before. The FBI’s 2025 Internet Crime Report logged 191,561 phishing and spoofing complaints, more than any other crime type, and about $3.05 billion in reported business email compromise losses.
Two official campaigns anchor the month. CISA runs “Securing the Next 250,” and the National Cybersecurity Alliance runs “Don’t Make It Easy for Them.” Both push the same four habits of corporate cyber hygiene: strong passwords kept in a password manager, multifactor authentication, spotting and reporting phishing, and updating software. The month dates to 2004, when the National Cybersecurity Alliance and the U.S. Department of Homeland Security launched it together.
Those habits stick when people do something, not when they read something. Attendance is not the goal. Participation is.
Why Traditional Cyber Education Falls Flat (And How Gamification Fixes It)
Before you build the October calendar, look at what breaks most awareness programs. Five failures show up year after year, and each one has an interactive answer.
Low Attendance at Optional Events
When attendance is optional, the people who need the training skip it. Daily work wins, and a slide presentation loses.
Word travels fast once a session is boring. You end up with a room of IT staff and two managers, while the people handling external email all day stay at their desks. Team scoring fixes that, because nobody wants to be the department that forfeited.
Fear-Based Messaging Causes Fatigue
Plenty of campaigns run on scary breach numbers alone. The threat is real, but telling staff that one wrong click sinks the company breeds anxiety, and anxious people stop listening.
Shift the tone from doom to action. Give people four habits they control, then let them prove the habits work in a format where getting it right earns points.
The One-and-Done Approach
Treating October as a checkbox creates a false sense of safety. Companies run one busy week, assign one video, then go quiet until the next autumn.
Habits need reinforcement. Without a plan to retest and revisit the core topics, October momentum is gone by Thanksgiving.
AI-Written Phishing Has Outrun the Slide Deck
The old tells are disappearing. Broken grammar and clumsy translation used to give a scam away, and generative tools erased both. Deepfake social engineering raises the stakes again, with a cloned voice on a phone call and synthetic video in a meeting invite.
A static deck written last year cannot keep pace with that. Live scenarios can, because you rewrite the questions the week you run them.
Hybrid and Remote Teams Never Get in the Room
Break room posters reach nobody working from a kitchen table. Hybrid workforce security engagement is its own problem: the staff most exposed to inbound email are often the ones furthest from the office.
Whatever you run in October has to work on a video call with the same energy it has on site, or half your workforce sits it out.
1. The Core 4 Kickoff Event (Week 1)
Open the month by naming the four habits both campaigns promote. Pull the free employer toolkits from CISA and the National Cybersecurity Alliance, which include posters, tip sheets, slide templates, and sample emails.
Put the materials in break rooms, on the intranet, and in your main Slack or Teams channel so remote staff get the same message. One clear message in week one sets the tone for the next three.
2. Phishing Spot-the-Fake Contest (Week 1)
Collect five to ten real phishing emails and post them beside legitimate company messages. Ask employees to flag the fakes and name the tell: the spoofed sender, the odd link, the manufactured urgency.
Include at least one AI-written example so the room learns that clean grammar proves nothing. Run it on a bulletin board or as a ten-minute opener at a staff meeting, because hunting the fake together beats grading people in private.
3. Password Manager Setup Clinic (Week 2)
“Use strong passwords” fails when nobody can remember them. Book one hour, station IT in the breakroom, and install the company-approved password manager on laptops as people walk up.
Remove the technical friction and adoption follows. One master password instead of forty is an easy sell.
4. Multifactor Authentication Enrollment Drive (Week 2)
CISA says users who enable multifactor authentication are significantly less likely to get hacked. Staff still treat it as an annoyance, so reward the people who move first.
Track which department hits full enrollment first and buy that team breakfast. Push authenticator apps instead of SMS codes while you have everyone’s attention.
5. Report-It Button Challenge (Week 3)
Recognizing a scam is half the job. Reporting it fast is the other half.
Send a harmless simulated phishing email that any attentive reader catches, then measure how many people hit the report button within the first hour. Name the fastest reporters and hand out a small prize.
6. Lunch-and-Learn Using the CISA Toolkit (Week 3)
Cater lunch and spend the hour on personal digital safety. The CISA slide templates cut prep time for your IT lead to minutes.
Tie every habit to home: the family bank account, the kids’ tablets, the shared streaming logins. Leave fifteen minutes for Q&A so people ask about their own devices.
7. Escape-Room Style Security Scenario (Week 3)
Build a tabletop exercise where small teams solve security puzzles to earn the next clue. They decode a password rule, find the rogue USB drive planted on a desk, and pick the right first move after a ransomware note.
People argue, test ideas, and remember the answer because they worked for it. That is the difference between a handout and an experience.
8. Cross-Department Security Leaderboard (Week 4)
Score every activity from the month and post a running leaderboard on the intranet. Award points for clinic attendance, contest entries, and reported phishing tests.
Visible progress starts friendly rivalries. Accounting will not want to lose to marketing, and your participation rate climbs on its own.
9. Live Security Trivia Game Show (Week 4)
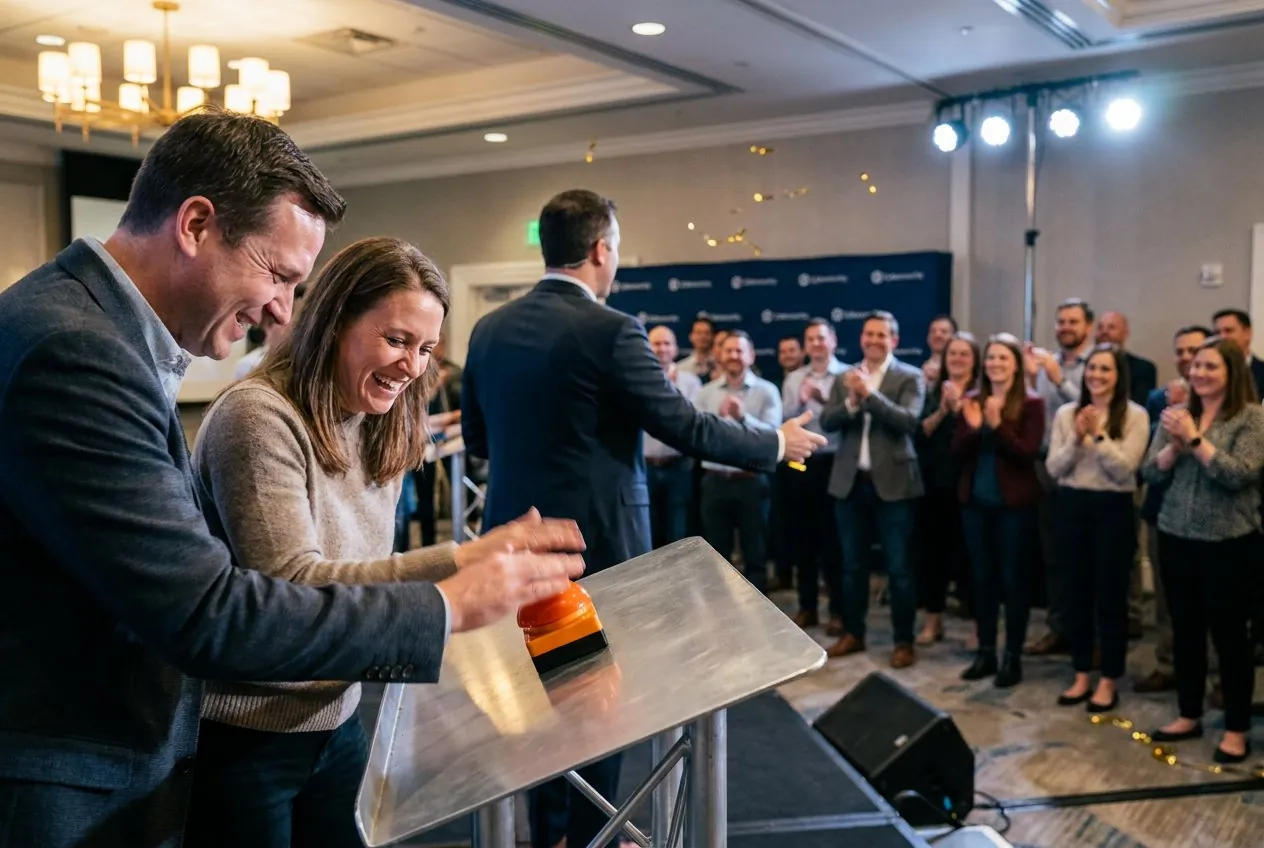
Replace the wrap-up lecture with live trivia, the same format as our office trivia games. Test the room on phishing tells, password rules, MFA basics, zero trust basics, and the official campaign themes.
Teams compete, the room gets loud, and the answers stick. A group laughing about authenticator apps is a group that learned something.
10. Wrap-Up Awards and Recognition (Week 4)
Close October by recognizing the people who showed up. Have an executive hand out certificates or prizes for the top trivia team, the fastest phishing reporters, and the first department at full MFA enrollment.
Public credit changes how next October feels. Employees look forward to the program instead of dodging it.
October Activity Formats Compared
Here is how the common formats stack up for a large group.
| Format | Group size | Setup load on your team | Who actually participates | Cost signal |
|---|---|---|---|---|
| It’s PlayTyme Game Shows hosted game show | 20 to 300+ | Low: we write it and host it | The whole room, on site or on video | Starting at $2,995 |
| Gamified security awareness training run by internal staff | Small teams | High: scripting, scoring, hosting | Mostly the confident volunteers | Internal staff hours |
| AI phishing simulation platform | Your full email list | Medium: setup and reporting | Individuals at their desks | Annual license |
| Slide-deck training session | Unlimited seats | Low | Few, and briefly | Internal staff hours |
| Lunch-and-learn | 10 to 60 | Medium: catering and a speaker | Attendees who ask questions | Catering plus staff hours |
Run It as a Live Game Show
Across more than 3,000 live events since 2012, It’s PlayTyme Game Shows has helped organizations across New Jersey, New York City, New York State, and Connecticut get large groups to connect. Fully hosted corporate event entertainment is how we do it.
We write custom questions with your IT or security team, so the trivia matches your actual policies and this year’s campaign themes. A live host runs the whole thing, in your office or over Zoom for a hybrid workforce, and a show fills 60 or 90 minutes for groups of 20 to 300+.
Great events are not measured by how many attend. They are measured by how many participate. Pricing is transparent, starting at $2,995, and no deposit is required. Your date is reserved once the signed performance agreement is returned.
Compliance Context for Tri-State Employers
Awareness activities and regulatory requirements are two different things. New York DFS-regulated financial companies must provide at least annual cybersecurity awareness training that covers social engineering for all personnel under 23 NYCRR 500.14(a)(3). Connecticut insurance licensees owe cybersecurity awareness training under C.G.S. 38a-38, and New Jersey has no equivalent general statute today.
Those rules bind regulated firms only. A trivia game or an activity fair does not make a company compliant. Interactive events reinforce your required annual training; they never replace it.
Measuring the Impact of Your Activities
Proving the month worked takes measurement, not vibes. The National Institute of Standards and Technology lays out the approach in NIST SP 800-50 Rev. 1 (2024), which names learning games and quizzes among practical exercises and treats a Cybersecurity Awareness Month activity fair as a valid awareness tactic.
In practice, test knowledge three times: before the campaign, right after it ends, and again a quarter later. Pair that with hard numbers like password manager enrollment and reported phishing tests, and you know which topics need attention in the spring.
Pick the October Activities Your Whole Workforce Will Actually Do
Match the format to your group size and your culture. For a small team with a confident internal host, gamified trivia run in house works. Above that, a professional host keeps 200 people on pace and on topic, and a hybrid audience needs a format built for a camera from the start.
Budget for a mix: technical clinics for the how, clear toolkit messaging for the what, and one high-participation event that gives the month a finish line. Choose the formats where everyone plays, not the ones where everyone watches. If you are also planning Halloween team building activities this fall, October lets you pair seasonal fun with a real company goal.
Ready to turn a required meeting into an event people want to attend? Contact our team to build a custom hosted game show for your organization.
Related reading
Frequently Asked Questions (FAQs)
What are the core themes for Cybersecurity Awareness Month?
Two official campaigns run side by side. CISA promotes “Securing the Next 250,” and the National Cybersecurity Alliance promotes “Don’t Make It Easy for Them.” Both center on four habits: strong passwords in a password manager, multifactor authentication, reporting phishing, and updating software.
How do you gamify cybersecurity awareness training for employees?
Turn the material into a scored competition. Put staff in teams, award points for spotting phishing tells and completing MFA enrollment, post a department leaderboard on the intranet, and close the month with live trivia written around your own policies. It works because people defend an answer out loud instead of clicking through a module alone.
What are some free cybersecurity awareness month activities?
The CISA and National Cybersecurity Alliance employer toolkits cost nothing and include posters, tip sheets, slide templates, and sample emails. A spot-the-fake bulletin board and a report-it button challenge need only staff time. Many teams run the free toolkit all month and save the budget for one hosted finale.
How long should a security awareness activity take?
Keep each one short. A password manager clinic or a spot-the-fake contest runs ten to fifteen minutes per person. A lunch-and-learn or a live game show runs 60 to 90 minutes, long enough to involve everyone and short enough to protect the workday.
Can interactive activities replace annual security training?
No. Game shows and contests reinforce required training; they do not substitute for it. Regulated companies, such as New York DFS-covered financial firms, still owe their formal annual training.
How do we measure the success of October security events?
Test knowledge before the campaign, immediately after, and a quarter later. Then track concrete numbers: password manager enrollment, MFA adoption by department, and how many simulated phishing emails get reported.